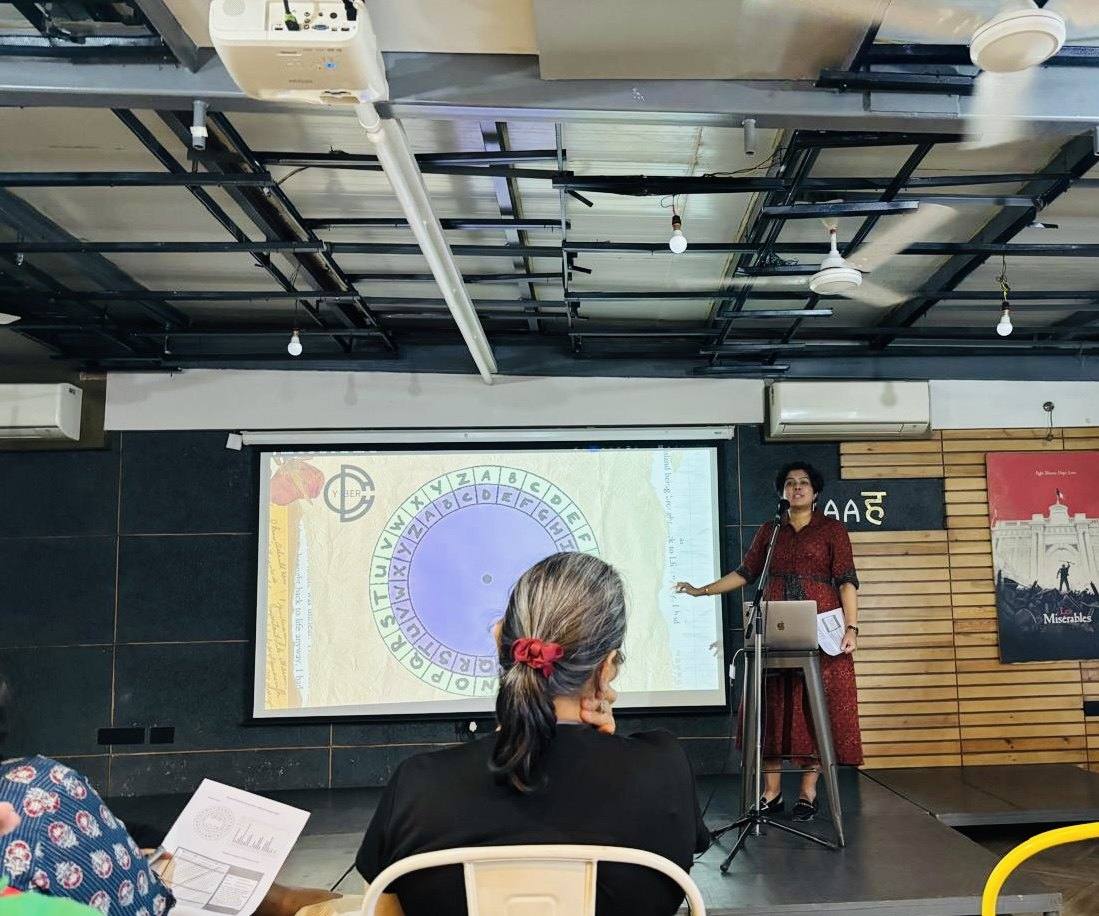
In July 2025 I ran an evening session at RAAH in Pune with an unusual title for a cybersecurity talk: “Password Security Through Storytelling”.
Why storytelling
Everyone has been told to use strong passwords. Almost no one enjoys hearing it again. The advice fails not because people are careless but because it arrives as a list of rules with no reason attached, and rules without reasons do not survive contact with a busy day.
So this session took a different route: the history of secret writing. Ciphers that armies and diplomats once trusted, how each was eventually broken, and what that tells us about the passwords we choose today.
Every code in history was broken by someone who understood how it was made. Passwords are no different.
From the cipher wheel to your inbox
Participants worked with a letter-shift cipher wheel, the kind of substitution code that feels unbreakable until you see how quickly patterns give it away. The same instinct that makes a shifted alphabet easy to crack — predictability — is what makes a password built from a name, a birth year and an exclamation mark easy to guess.
From there the practical part follows naturally:
- Length beats complexity: a long passphrase is stronger and easier to remember than a short jumble.
- Never reuse a password across accounts, because one breach then becomes many.
- Use a password manager, so you only have to remember one good secret.
- Turn on multi-factor authentication, which keeps a stolen password from being enough.
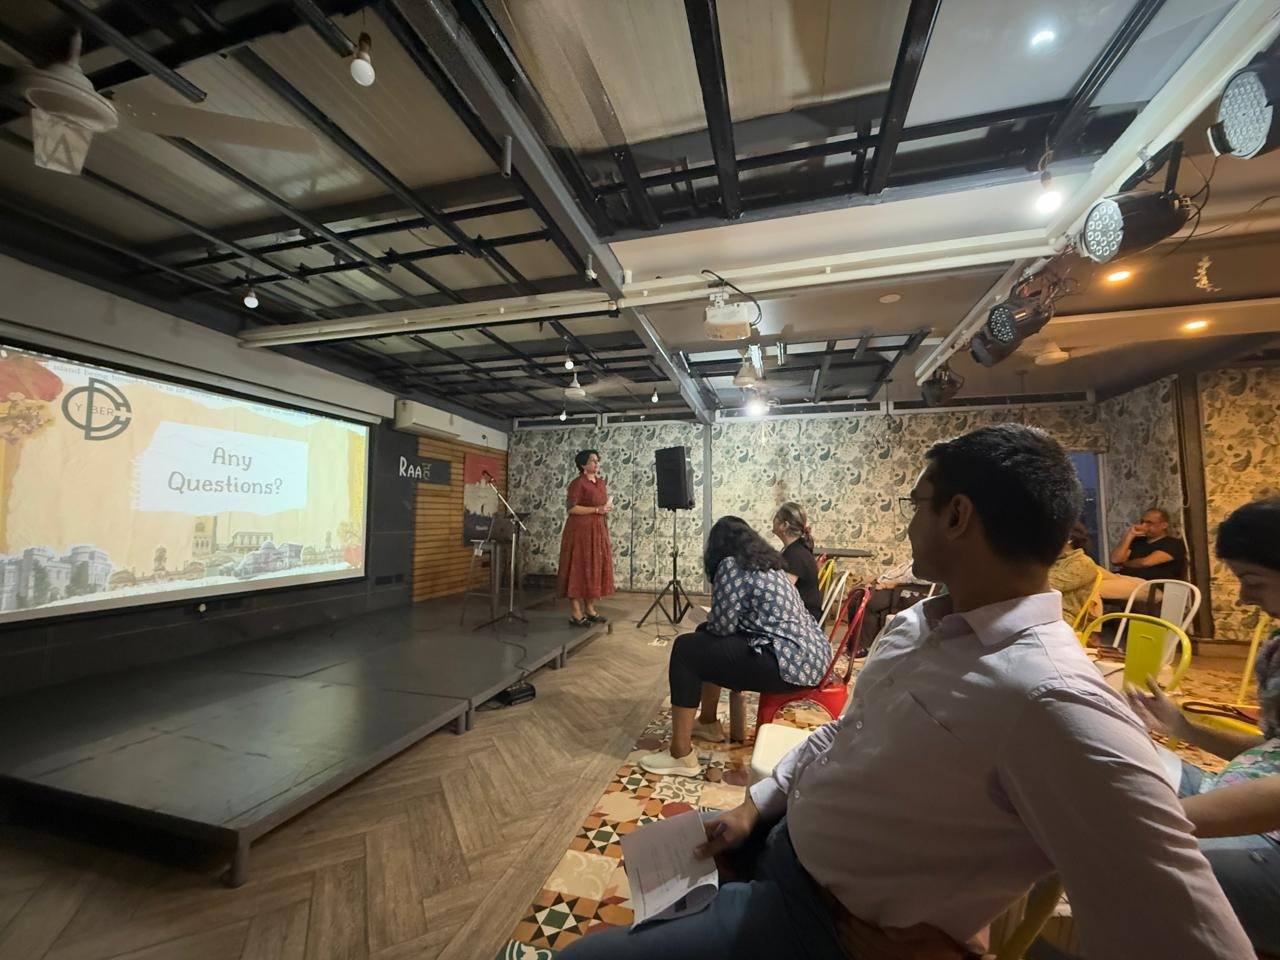
Thank you to RAAH for hosting, and to an audience that asked better questions than most professional workshops manage.
Bring this session to your organisation
We deliver awareness lectures, workshops and certified training for universities, government bodies and industry.
Talk to us Cyber awareness training