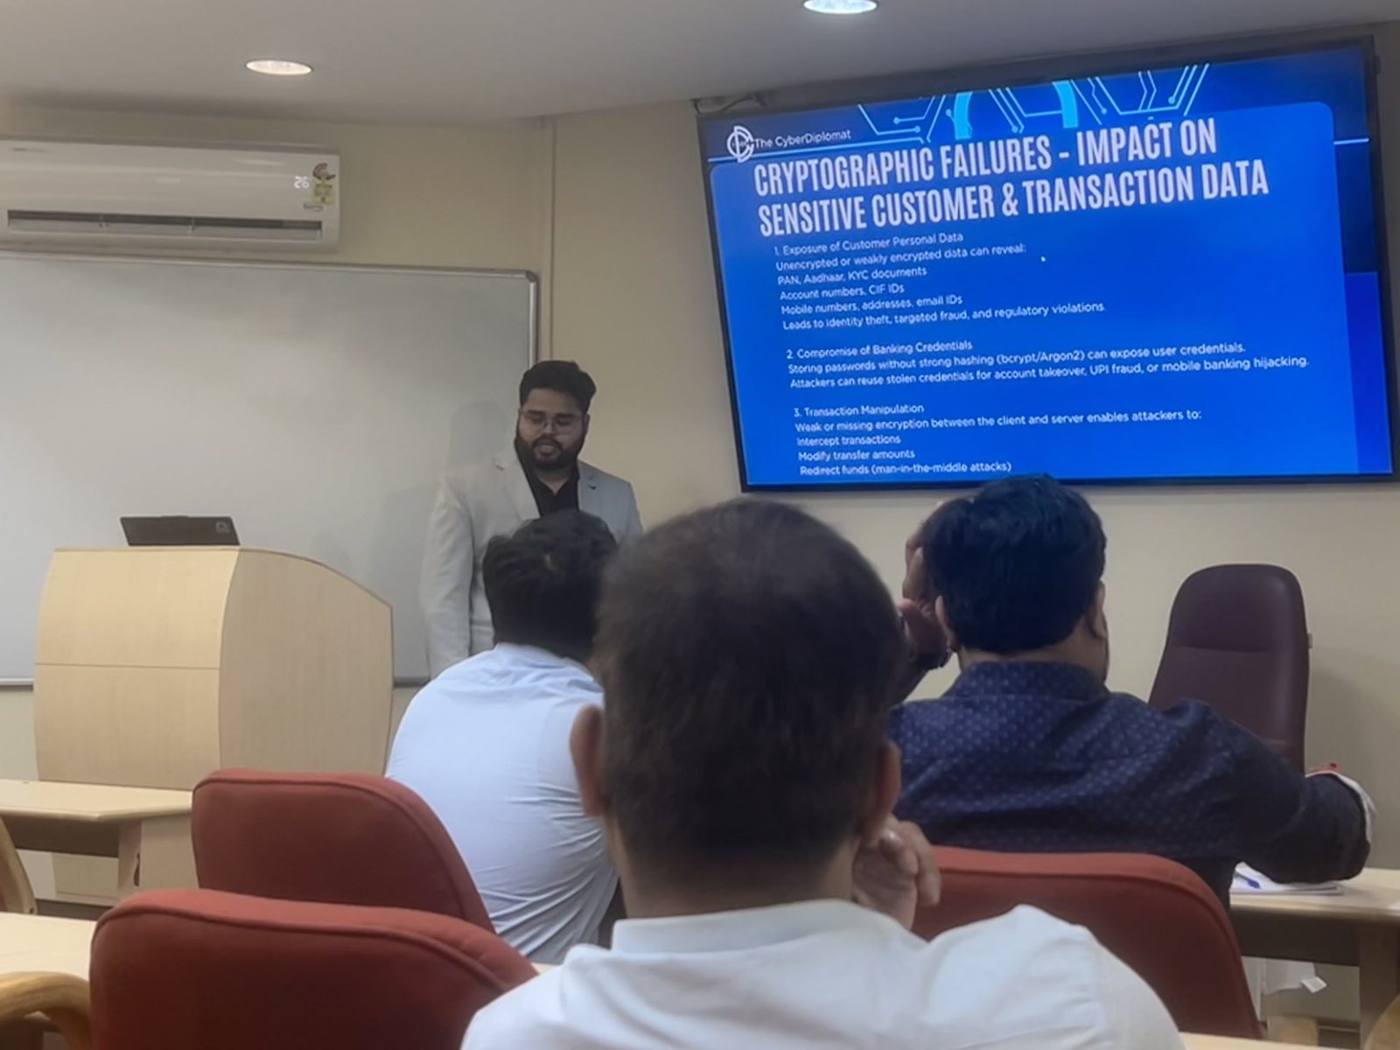
The CyberDiplomat delivered a technical cybersecurity training programme for banking officials at a banking institute, covering the security failures that put customer and transaction data at risk.
Cryptographic failures, in plain terms
One module of the programme dealt with cryptographic failures — what happens when sensitive data is not encrypted properly, or is protected with methods that no longer hold. For a bank the consequences are concrete:
- Customer data exposure: unencrypted or weakly encrypted records can reveal identity documents, account numbers, phone numbers and addresses — the raw material for identity theft and targeted fraud.
- Credential compromise: passwords stored without strong hashing can be recovered and reused for account takeover, UPI fraud or mobile banking hijacking.
- Transaction manipulation: weak or missing encryption between client and server allows an attacker to intercept transactions, alter amounts or redirect funds.
In banking, a cryptography mistake is not an abstract weakness. It is a customer’s money and a regulator’s attention.
Why banks need their own training
Generic security awareness does not serve a bank well. Banking teams work under specific regulatory obligations, specific incident-reporting timelines and specific fraud patterns. Training has to be built around their systems, their data and their duties — which is how this programme was designed, and how we build every banking engagement.
If your institution needs training of this kind, our training programmes cover secure development, OT and ICS security, ISO/IEC 27001 and governance, risk and compliance.
Bring this session to your organisation
We deliver awareness lectures, workshops and certified training for universities, government bodies and industry.
Talk to us ISO/IEC 27001 training